

AI raises cyber risk as firms race to boost resilience
Thu, 8th Oct 2026 (Today)
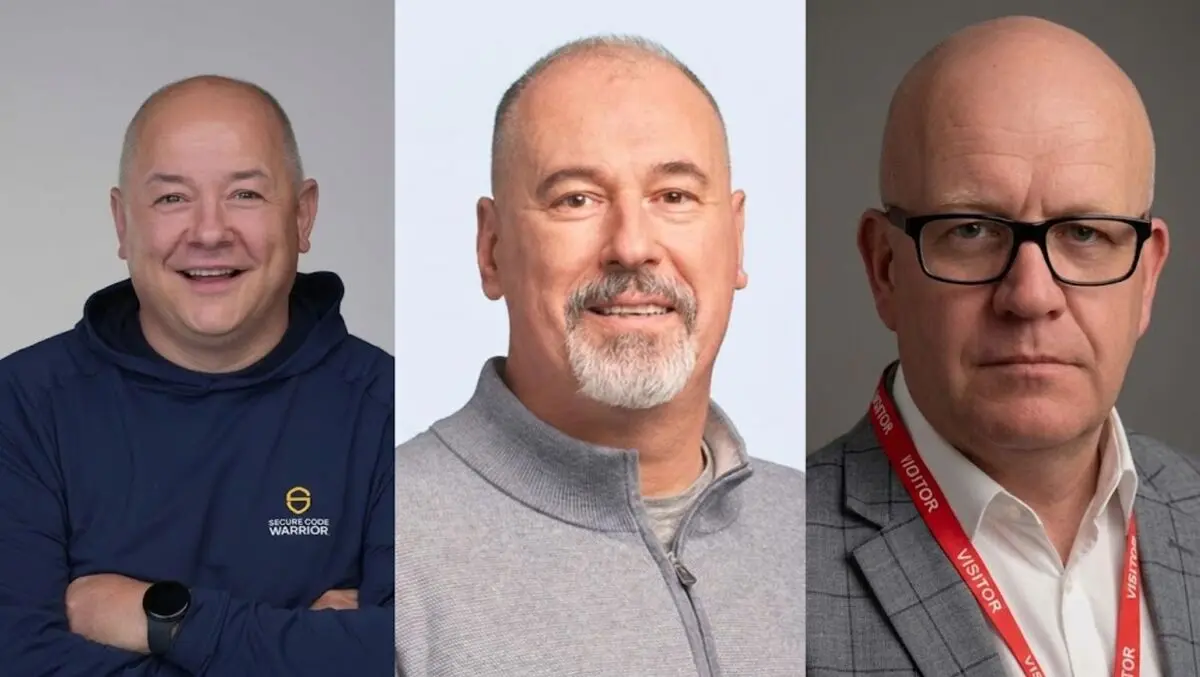
Hitachi Vantara and Secure Code Warrior warned that the spread of AI is reshaping cyber risk for organisations during Cybersecurity Awareness Month.
Both said attackers are using AI to move faster and scale up attacks. They also warned that companies are under pressure to strengthen data governance and recovery planning as regulators sharpen their focus on operational resilience and data handling.
At Hitachi Vantara, the emphasis was on data resilience rather than prevention alone. Its executives argued that boards should treat recoverability and business continuity as core parts of cyber risk assessment.
"Over the last year, cyber risks have increased as AI capabilities have become more sophisticated, giving threat actors new ways to identify vulnerabilities faster and launch attacks on a broader scale. At the same time, data governance is taking on greater importance amid sovereignty concerns and international regulations like DORA, NIS2 or GDPR. Protecting that data and ensuring it remains available and recoverable needs to be the top priority for any board or leadership team. This requires organisations to think beyond prevention and prepare for how they will maintain business continuity and recover trusted data when an attack occurs," said Octavian Tanase, Chief Product Officer, Hitachi Vantara.
Tanase said cyber resilience should be built into data infrastructure from the outset. Organisations, he said, need confidence that they can quickly restore trusted data if a critical system is compromised.
"Cyber resilience starts with a strong data foundation and clear governance, and it needs to be built into your data infrastructure from the start. If critical data is compromised, organizations need to know they can recover trusted data quickly and keep the business running. Planning for that recovery in advance is critical to maintaining business continuity and customer trust," said Tanase.
He also pointed to layered defences including immutable snapshots, anomaly detection, automated recovery and air-gapped environments, framing resilience as a practical recovery issue as much as a security one.
"Building cyber resilience into infrastructure means giving organisations multiple layers of protection, detection and recovery, from immutable data snapshots and anomaly detection to automated recovery processes and air-gapped environments. The goal is not simply to withstand an attack, but to be ready to restore trusted data and operations as quickly as possible when disruption occurs," said Tanase.
AI and Control
Chris Millington of Hitachi Vantara said AI has increased the pace of attacks, but argued that companies can also use it to improve visibility across their environments. He added that human oversight remains essential in incident response and governance decisions.
"AI has accelerated the speed at which attackers can operate. Although this isn't necessarily new, organisations can use AI themselves to better understand these risks and their exposure across their infrastructure, while helping to shape a new security and governance approach. For example, it can help automate a response against a malicious attack and then suggest what needs to be done to eradicate it. However, the decision-making process must still be left to humans," said Chris Millington, Global Solutions Lead, Data and Cyber Resilience, Hitachi Vantara.
Millington also argued that security strategies should centre on data. Organisations are better placed to maintain business continuity, he said, when they know where data sits, who owns it and what risks apply to it.
"Security isn't always about infrastructure; but it should always be about the data. If you know where your data is, the level of protection it has, who is responsible for it and the risks associated with it, your chances of successfully maintaining business continuity are much greater," said Millington.
He outlined three priorities for securing AI systems: data governance, zero-trust controls and the use of AI in defensive operations under human control.
"Third, using AI as part of your defence strategy. This isn't about letting AI systems make decisions autonomously. Rather it focuses on turning the same technology adversaries use against them, while keeping it aligned with security processes and under human control," said Millington.
Wider Surface
Secure Code Warrior focused on the impact of generative AI on software creation. Pieter Danhieux said the rise of AI agents, low-code tools and business-led application development has changed who writes and commits code inside organisations.
He said that shift has expanded the attack surface beyond traditional engineering teams. In his view, the issue now extends to staff in business functions using AI tools to create workflows, integrate systems and deploy applications.
"We cannot bridge an AI security and literacy gap through passive governance policies or automated scanning alone. In a new, pervasive workflow where AI agents generate code, review pull requests, and trigger deployments, securing what the AI misses becomes the chief focus for every human across the organisation. At the same time, we need to get comfortable, very quickly, with the fact that the enterprise attack surface has fundamentally expanded forever, because the definition of who actually 'commits code' has changed. With the rise of generative LLMs, low-code/no-code platforms, and agentic assistants, software creation is no longer restricted to the time-honoured engineering departments of old. Today, business users across finance, HR, marketing, and operations (our 'citizen developers') are building custom workflows, integrating APIs, and deploying applications directly into fundamental business functions. If organisations want to maintain control over the attack surface, all staff who generate or commit code with AI, from seasoned software engineers to business citizen developers, must possess verifiable security skills, both in the context of their roles, and within the tools they are using. Organisations must equip every employee with the practical judgment needed to audit AI outputs, manage credentials safely, and identify security flaws before code reaches production. That is why this Cybersecurity Awareness Month we encourage security leaders to move beyond static awareness and build real, verified defence capabilities across their workforce," said Pieter Danhieux, Co-Founder and CEO, Secure Code Warrior.