

SHI warns firms to prepare for quantum security risks
Tue, 29th Sep 2026 (Today)
SHI has urged organisations to prepare for the security risks posed by quantum computing, warning that companies need greater crypto-agility across their technology systems.
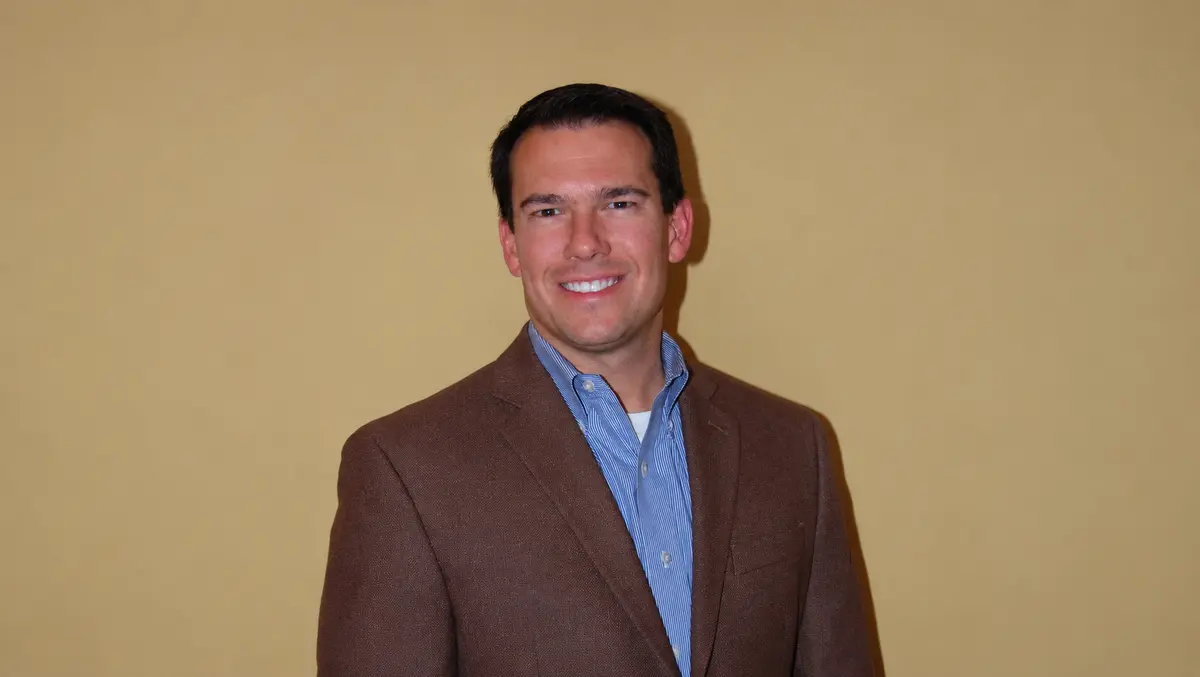
Brad Bowers, Lead Field CISO Global at SHI, said businesses could face a narrow window to replace vulnerable cryptographic systems if quantum computing advances at the faster end of current forecasts.
He pointed to the debate over the timing of so-called Q-Day, when quantum computers become powerful enough to break parts of the public-key cryptography widely used in digital security. Estimates vary. The US National Institute of Standards and Technology has suggested a timeframe of 2030 to 2035, while Google has projected a date closer to 2029.
Bowers also highlighted IBM's planned Starling quantum computer, expected to debut in 2029 as a fault-tolerant system capable of executing up to 100 million quantum operations.
Migration challenge
For companies, the main concern is not a single breakthrough but the time needed to respond. Replacing cryptographic systems across large organisations can take years because encryption is embedded in applications, networks, databases, identity systems, connected devices and business processes.
That makes preparation a board-level issue, particularly for businesses with large and complex estates. Organisations that wait could struggle to complete migrations before quantum threats become practical.
"Exactly when Q-Day will arrive remains a matter of debate. Q-Day refers to the point at which quantum computers become powerful enough to break components of public-key cryptography that underpins much of today's digital security. The National Institute of Standards and Technology has suggested this could happen between 2030 and 2035, while others, including Google, have publicly projected a date closer to 2029. Not coincidentally, IBM's Starling quantum computer, a fault-tolerant system designed to execute up to 100 million quantum operations, is also expected to debut in 2029, providing the quantum compute power to pose a significant risk to businesses worldwide. If the more aggressive timelines prove accurate, many organisations may find themselves behind the proverbial eight-ball.
"Transitioning enterprise cryptography is not an overnight exercise. Large-scale technology transformations typically take three to five years, and in some environments significantly longer. Waiting until Q-Day is on the doorstep will be far too late. That is why organisations should be laying the groundwork now. Becoming quantum-ready, or more specifically crypto-agile, deserves executive attention today. In fact, the issue may ultimately prove more consequential than many of the AI initiatives that have dominated boardroom and CISO conversations over the past several years," Bowers said.
The issue is especially visible in sectors with strict regulatory demands or critical infrastructure responsibilities. In those environments, many organisations have already begun assessing their exposure, setting migration plans and considering how to protect sensitive data against long-term risks.
One of those risks is known as harvest now, decrypt later, in which attackers collect encrypted data today in the expectation that future quantum systems may be able to unlock it. The threat is most acute for information that retains value over long periods.
Finding weak points
Bowers said the practical starting point is discovery: identifying cryptographic dependencies across the estate, understanding which algorithms are in use and deciding which systems need priority treatment. That is often difficult because many businesses lack a complete inventory of where encryption is embedded.
He described crypto-agility as the ability to identify cryptographic dependencies, assess the risks attached to them and replace weak algorithms with approved alternatives as standards change. It also includes compensating controls for systems that cannot easily be upgraded or replaced.
"Organisations operating in heavily regulated industries or supporting critical infrastructure generally understand the challenge. Many are already assessing their exposure, building migration plans and evaluating how to defend against 'harvest now, decrypt later' attacks, where threat actors collect persistent-value encrypted data today with the expectation that future quantum capabilities will allow them to decrypt it. Outside those sectors, however, the urgency is often less apparent.
"So what does crypto-agility actually mean? At its core, it is an organisation's ability to identify where cryptographic dependencies exist, understand the risks they create and replace vulnerable algorithms with approved alternatives as standards and requirements evolve. It also means having compensating controls in place for systems that cannot easily be upgraded or replaced.
"The challenge is that no organisation has complete visibility into where cryptography is embedded across its environment. Encryption is woven throughout applications, operating systems, networks, databases, identity systems, connected devices and business workflows. Before organisations can migrate to post-quantum cryptography, they must first understand through discovery where vulnerable algorithms are being used, assess the potential impact of a compromise and prioritise remediation efforts. The scale and complexity of that task should not be underestimated," Bowers said.
The argument extends beyond end users to software developers and technology suppliers. Systems built now may need to support algorithm changes later without broad rewrites or disruptive overhauls, especially as post-quantum standards continue to mature.
AI and standards
Bowers cited recent work by Anthropic's Claude model, which identified weaknesses in the HAWK algorithm, one of the candidates proposed for the post-quantum era. He said such findings should not be seen simply as a sign of weakness in post-quantum cryptography, but as evidence that new tools are testing the resilience of emerging standards.
The broader point, he said, is that no cryptographic standard remains secure indefinitely. If one post-quantum algorithm later proves vulnerable, organisations will need to move again, making flexibility in system design a central requirement rather than a technical preference.
"This is also a call to action for software developers and technology vendors. Future applications should be designed with crypto-agility in mind, allowing cryptographic algorithms to be updated or replaced without major code changes or disruptive system overhauls. Even then, there are no guarantees. Cryptography has always evolved in response to new discoveries and new attack techniques.
"Recently, Anthropic's Claude model identified cryptographic weaknesses in the HAWK algorithm, one of the candidates proposed for the post-quantum era. Some observers have interpreted findings like this as evidence that post-quantum cryptography remains immature. I would argue the opposite. The fact that AI can be used to stress-test and scrutinise these algorithms should be seen as a strength, not a weakness.
"At the same time, it reinforces the importance of crypto-agility. No cryptographic standard is guaranteed to remain secure forever. If a post-quantum algorithm is later found to be vulnerable, organisations will need the ability to transition quickly to an alternative. Those that have built crypto-agility into their architecture will be able to adapt. Those that have not may find themselves facing another costly and complex migration under significant time pressure," Bowers said.